Machine-to-Machine
Identity Management for
Automated Services
Unified access control for your scripts, agents, daemons, and micro services
across your entire tech stack with ease.
How It Works
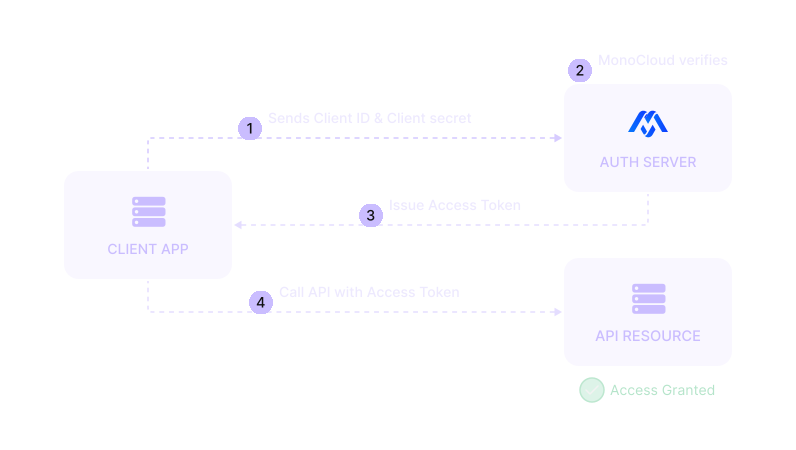
M2M Authentication Flow
M2M authentication protects your APIs by ensuring only verified machines can access them.
Secure API Access
Zero-Friction API Management
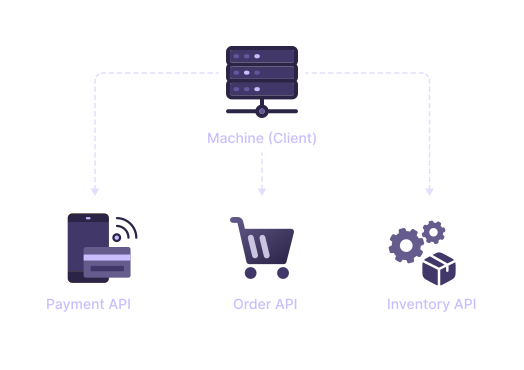
Define your internal APIs as secure resources and issue granular permissions.
Ensure your backend services, daemons, and microservices only access exactly what they need to function.
mTLS Authentication
Certificate-Bound Security
By using certificates, your services prove who they are during the initial handshake
MonoCloud replaces vulnerable bearer tokens with certificate-bound credentials that only function when presented by the specific client that requested them.
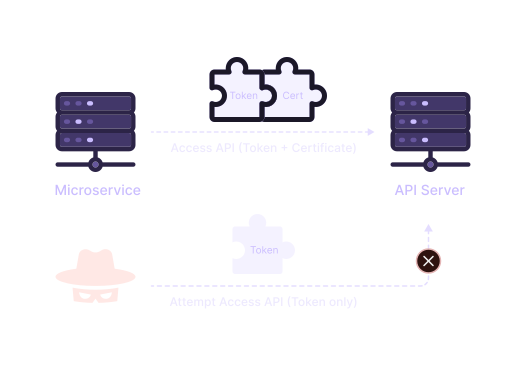
Give every service its own identity, not a shared secret
Book a demo, or start free today.