Resource Protection
Holistic API Governance
& Security
Implement defense-in-depth with fine-grained resource protection and visibility for API requests.
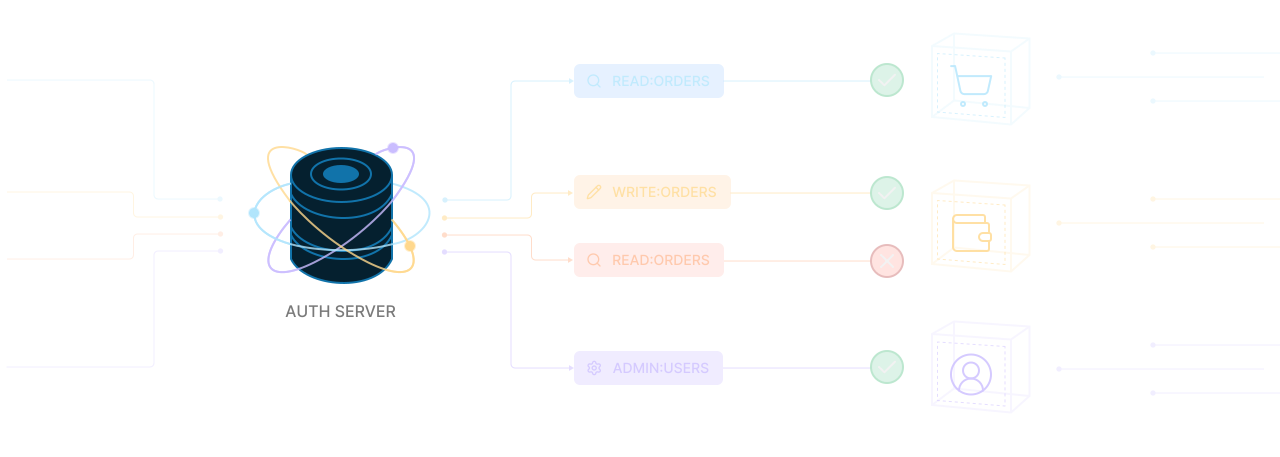
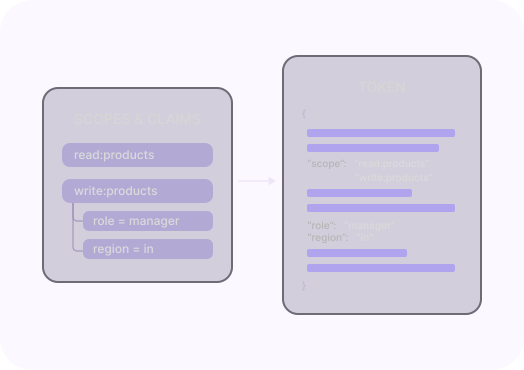
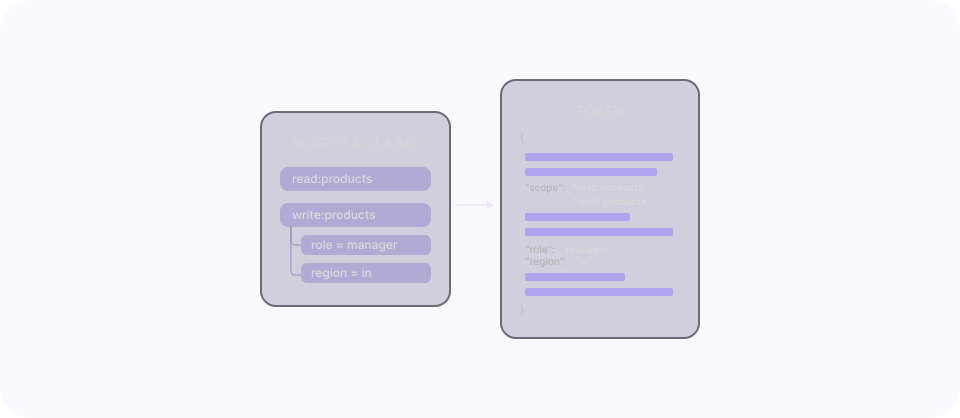
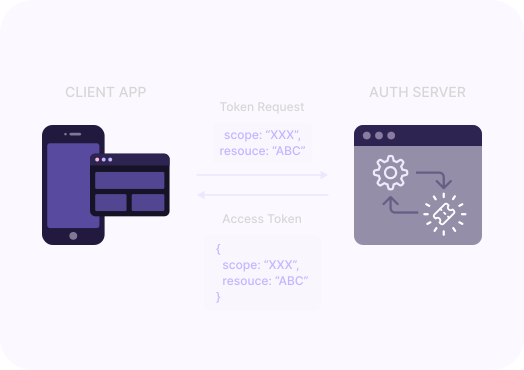
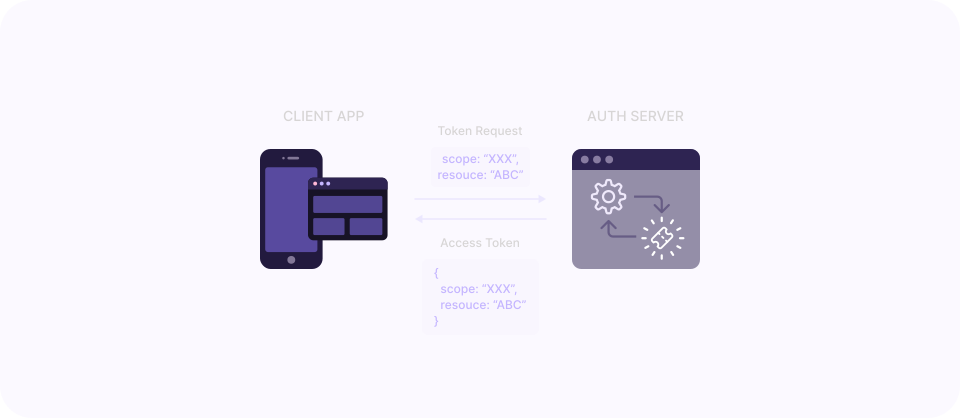
Customizable Token
Fine Grained Auth for API
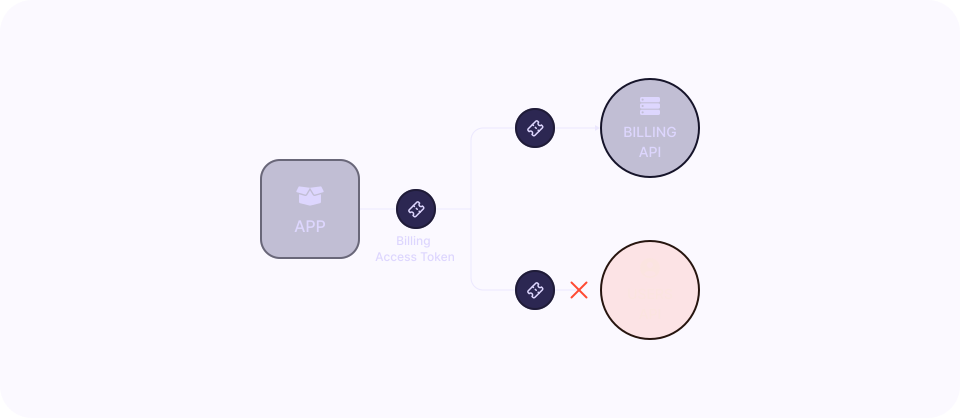
Enforce strict boundaries and rich context with fully customizable, resource-specific access tokens.
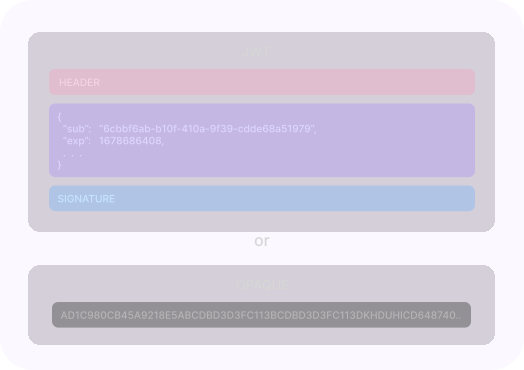
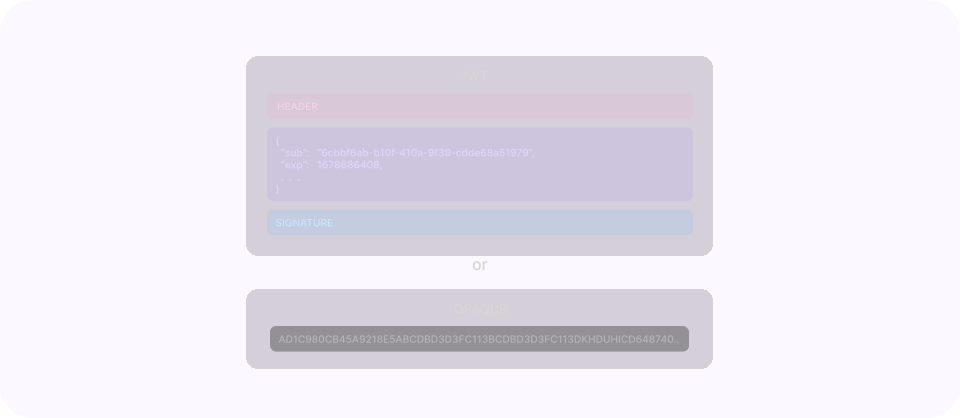
Zero Trust Security
Uncompromised API Security
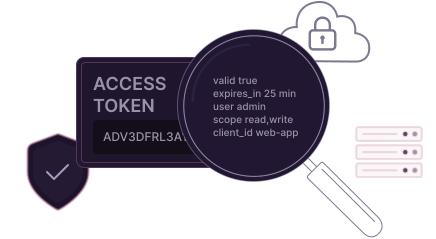
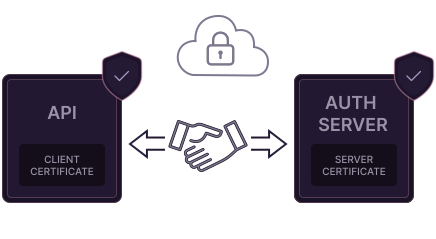
Enforce real-time API security via Token Introspection, and ensure strict transport
security via mTLS.
Token Introspection
mTLS Authentication
Access Control
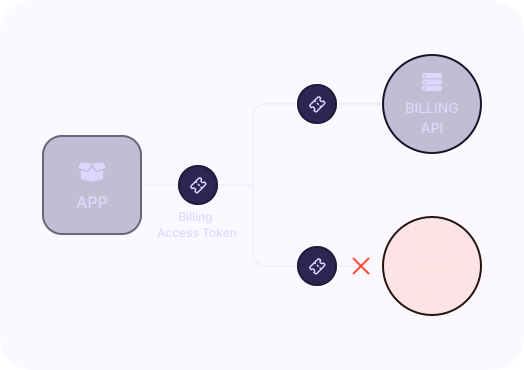
API Access Control
Explicitly map and enforce exactly which client applications are authorized to consume
specific API services.
Simplified Application-to-API Access Mapping
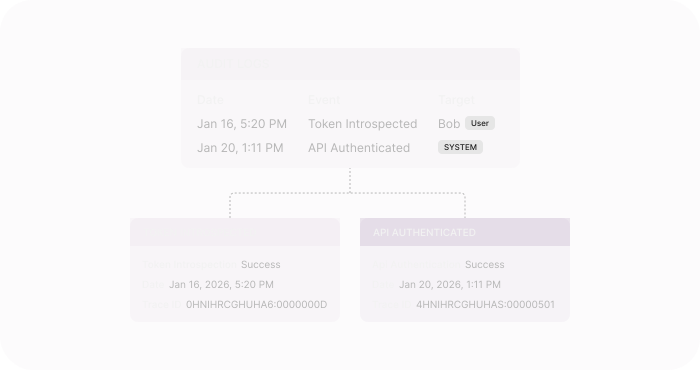
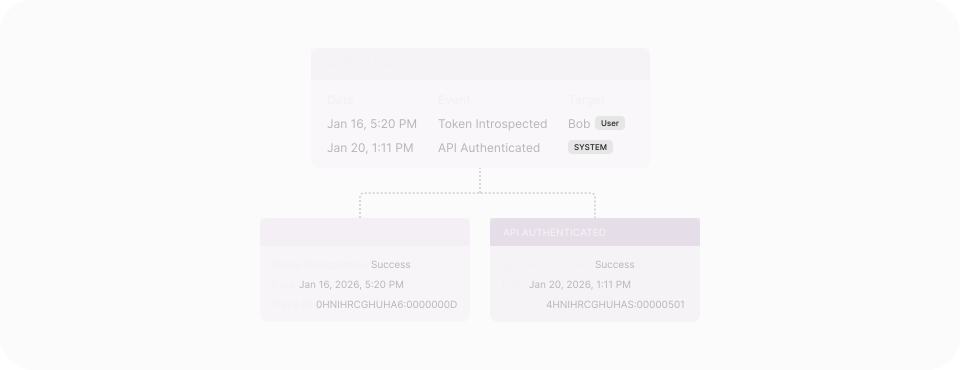
Full Visibility
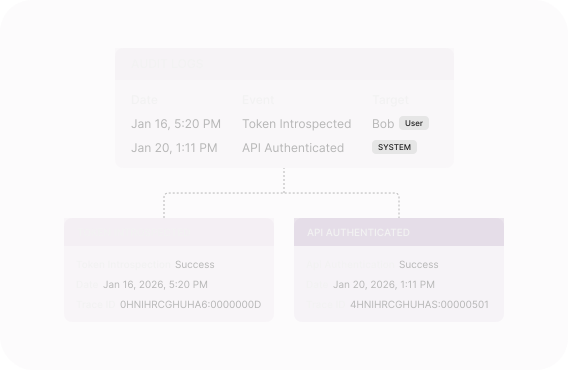
Token Issuance and Introspection Logs
Ensure accountability and compliance by logging the lifecycle of every token, from initial issuance through active use to revocation.
Resource protection, answered
FAQs, answered
What teams ask before putting fine-grained protection in front of their APIs.
Why is Token Introspection safer than local validation?
Local validation relies on expiration times. Introspection checks the server in real time, so you can immediately reject revoked tokens even if they have not yet expired.
What is Application-to-API Access Mapping?
It is an explicit allow list between clients and APIs. Each application is authorized for named resources and scopes, so an app can only request tokens for the APIs you mapped it to.
How does this help with compliance audits?
Every issuance, introspection, and authentication event is logged with a timestamp and trace ID, giving auditors a complete record of who accessed which resource and when.
Does real-time introspection slow down my API?
Introspection responses are cached for a configurable window, so most requests are validated locally while revocation still propagates within seconds.
Can I block a specific application without banning the user?
Yes. Access is mapped per application, so you can revoke or narrow one client’s resource access while the same user keeps working through your other apps.
Put a policy checkpoint in front of every request
Book a demo, or start free today.